example.test
DNSwwwAPI
 Illustration of a working environment
Enrolment opening soon
Pentester tools and operations
Connect pentesting tools into a deliberate workflow: from service discovery to validation, documentation and closure. Practice relationships between commands, sessions and permissions in a controlled training environment. Choose the next step from the previous result.
PLN 599planned price including tax
In your browser · No installation · Tutor and narration
Open your browser. Start learning.
Do not spend your first evening configuring an environment. The application, tools and task context are in one place. You do not need Docker, a VPN, a virtual machine or paid software.
A virtual tutor walks you through the example and highlights important parts of the application, code or tool. Connect the instruction to what is happening on screen.
Narration explains the mechanism, decision and result. Pause the guidance, return to an earlier step and work through it at your own pace.
Take over in the exercise: change data, run a test or make a decision. Compare the result and improve your solution using the explanation.
One environment, without switching between a video and a local installation. Tools fit the topic: from HTTP requests and code to a terminal, calculator or document. Practice in simulators and prepared cases, without attacking other people's systems.
What will you be able to do?
Connect reconnaissance, validation, session state and closure into a controlled workflow.
You know tool names but not which one to use now.
Justify the command, required access and expected signal. Identify when a result needs another check.
An open port or scanner result immediately becomes a vulnerability.
Connect the discovered resource to a protocol observation and a specific hypothesis test. Distinguish a lead from a confirmed issue.
After a successful attempt, you do not know what remains in the environment.
Document operations, check cleanup in the scenario and prepare retest conditions.
Prepare to use tools in an authorized engagement. Training models teach dependencies and decisions; they do not replace practice with every real tool.
Connect each skill to a concrete work product. Return to explanations while you practice.
A syllabus backed by materials
See what makes up the syllabus: lessons, explanations, examples and exercises. The figures below describe different types of materials.
The figures describe the English-language source materials. The waiting list is for the planned Polish edition. These counts do not mean its translation is complete. Demonstration steps, examples and tasks are different units, not hours of video or counts of unique vulnerabilities.
Entry point
Available in Polish and English — you can switch language at any time. Command names, code snippets and standard identifiers remain in their original form.
How you learn
The tutor walks through an example and explains each decision. In the exercise, return to the context, check the result and improve your answer.
Goal, constraints and inputs. Know what you are testing and why.
Watch a demonstration with tutor commentary, step by step.
Work with data, a tool or a scenario. Compare the result with your expectation.
Justify your decision and understand its limitations. Return to anything that needs improvement.
Exercises use simulators and selected mechanisms that run in the browser. They do not require attacking other people's systems.
Planned syllabus
Each area develops a specific skill. Learn not only the topic but also the action and outcome that learning leads to.
Each topic includes a skill and a concrete exercise outcome.
I want to join the listRead engagement rules, exact targets and exclusions. Build reconnaissance from a name through DNS and TLS to a service in the prepared environment. Connect every next step to authorization and the question it answers.
Case analysis
Compare information available through HTTP, SSH, SMB and LDAP. Distinguish an open port, service response and confirmed permission. Choose further analysis for the protocol and available context.
Demonstration with explanation
Build a pipeline from resource names through port discovery to HTTP enrichment. Preserve intermediate results and check that the next tool receives the correct data. Prepare a record explaining both hits and missing results.
Tutor-guided exercise
Analyze supplied audit material, including synthetic hashes and tool results. Choose a condition that confirms or challenges a scanner hypothesis. Connect the signal, verification and cause instead of passing on an alert alone.
Tutor-guided exercise
Trace module preparation, option setting, prerequisite checks and session handling. Exercises use an explicit tool-state model, including Metasploit, to teach dependencies and decisions. Record created resources and close your own actions in a controlled way.
Demonstration with explanation
Use a Linux permissions example to identify the enabling condition, minimal validation and cause removal. Analyze supplied traffic with provenance information. Correlate events and times without presenting the file as your own capture.
Case analysis
Practice access through an authorized route to another segment and compare state before and after the change. Connect Kerberos, LDAP and SMB information to the identity model. Analyze AWS and Kubernetes authorization decisions without collecting secrets or modifying external infrastructure.
Case analysis
Combine reconnaissance, validation, sessions and documentation from a clean baseline. Prepare a minimal observation package and close exercise-owned processes and sessions. Finish with rejection of an unauthorized action and a legitimate-use control.
Tutor-guided exercise
In practice
Each case has context, a concrete action and an outcome. The goal is not to memorize a command but to understand why the result changed.
Combine DNS reconnaissance, service discovery and HTTP responses into one workflow. Preserve intermediate results, choose authorized validation and compare the result with the tool's hypothesis.
Work productA documented reconnaissance workflow with reasons for subsequent actions.
In the modeled environment, trace option preparation, session state and minimal permission validation. Record and close your own resources, then test the fix alongside legitimate service use.
Work productAn operations record, cleanup confirmation and final test set.
Certificate of completion
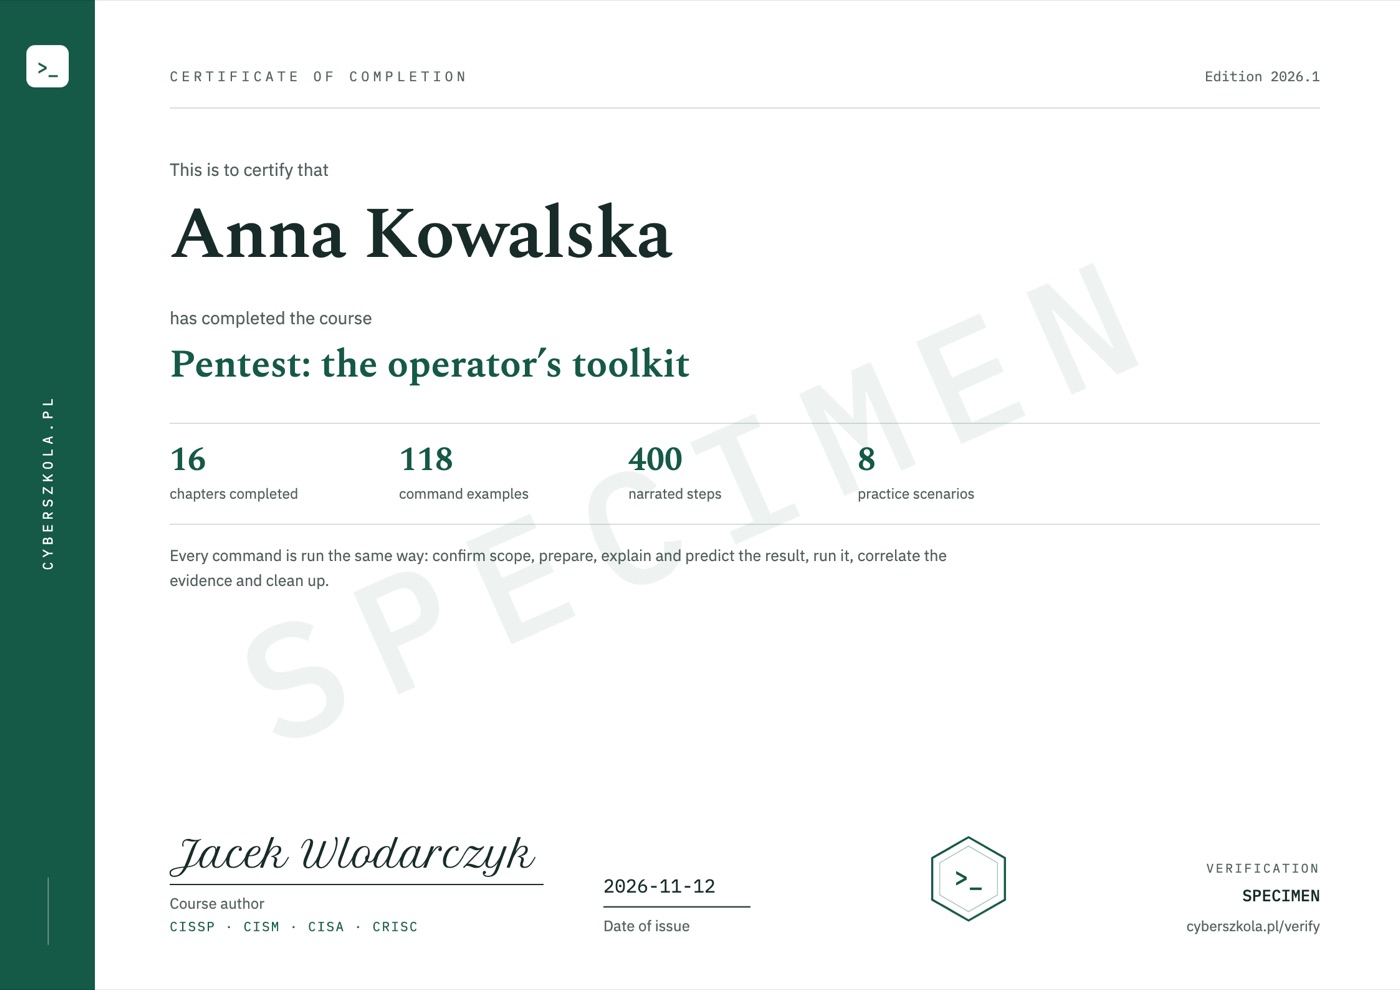
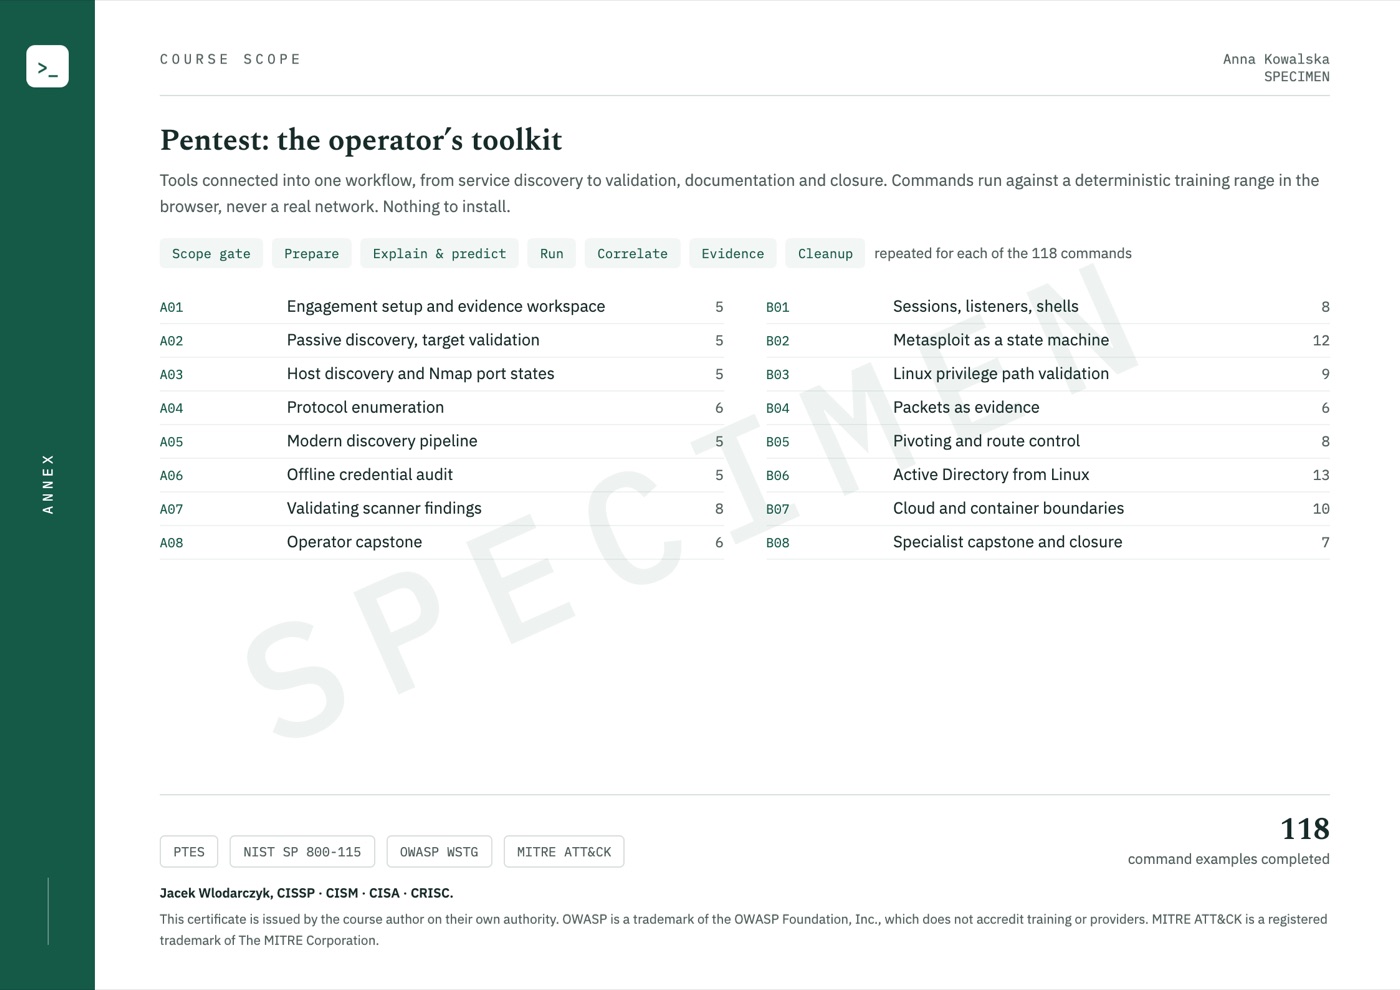
When you complete the course, the certificate is issued automatically and emailed to you. It shows your name, the date of issue and a unique code, and its second page lists the course scope.
Code verification: cyberszkola.pl/verify
Upcoming standalone course
Planned course price
Polish edition · Launch date not yet announced
Notify me at launchJoining is free. Before sales open, you will receive the date, full scope and purchase terms. We are not taking payments today. This is a separate interest list, not a place reservation or purchase.
For companies and teams
Compatible with LMS platforms including:
and other platforms that support e-learning standards.
Price for companies
Delivery into your company's own LMS from 50 licences.
Ask for a quoteWrite to [email protected]: the number of people, the courses you want and your LMS, if you use one.
Project author
Creator of Cyberwiedza, cyberszkola and AI SecLabs. In these courses, I connect explanations of mechanisms with practice, observation and decisions you need to justify.
Running a command is not enough. What matters is what its output confirms, what it does not confirm and what the next step should be.
More about the authorBefore joining
No. The course uses controlled tool models and prepared materials to teach decisions, dependencies and result interpretation. It does not present these exercises as running a full toolset against external infrastructure.
Recon focuses on sources, logs, integrity and result handover. The pentester toolkit extends this to protocols, sessions, permissions and tool dependencies while retaining documentation and cleanup requirements.
No. This is an upcoming course announcement and an interest list. Joining is not a purchase, a place reservation or a commitment to pay.
The launch date, price and access terms will be announced before sales open. The interest list is how we send that information.
The course is available in Polish and in English — you can switch language at any time, and lessons, exercise explanations and narration exist in both. Commands, code and tool names keep their original syntax, as used in everyday work.
No. All course exercises run in your browser on a computer with internet access. Training applications, terminals, editors and workshops are part of the platform. You do not install Docker, a virtual machine or a VPN, and you do not need paid external tools.
No. You work in an interactive environment. A virtual tutor highlights important elements, and narration explains the action and its result. Pause the lesson, return to earlier steps and run your own experiments. This guidance is built into the course, not individual consultation with a person.
No. You use training applications, simulators and prepared data. Learn the mechanism and its limitations in a safe environment. External resources are supplementary, not required to complete the exercises.
Yes, a certificate of completion. When you complete the course, you receive a certificate in English with a unique code that anyone can check at cyberszkola.pl/verify. It confirms completion of the course and is issued by the author; it is not an industry certification. We do not promise employment.
No. These are independently authored courses using public references and original cases. They do not replace licensed standards, accreditation or qualifications required in regulated industries.
Join the waitlist
Leave your email address. We will send you news of enrollment, the syllabus and first-edition terms. You will not need to keep checking this page.
Planned price: PLN 599 including tax